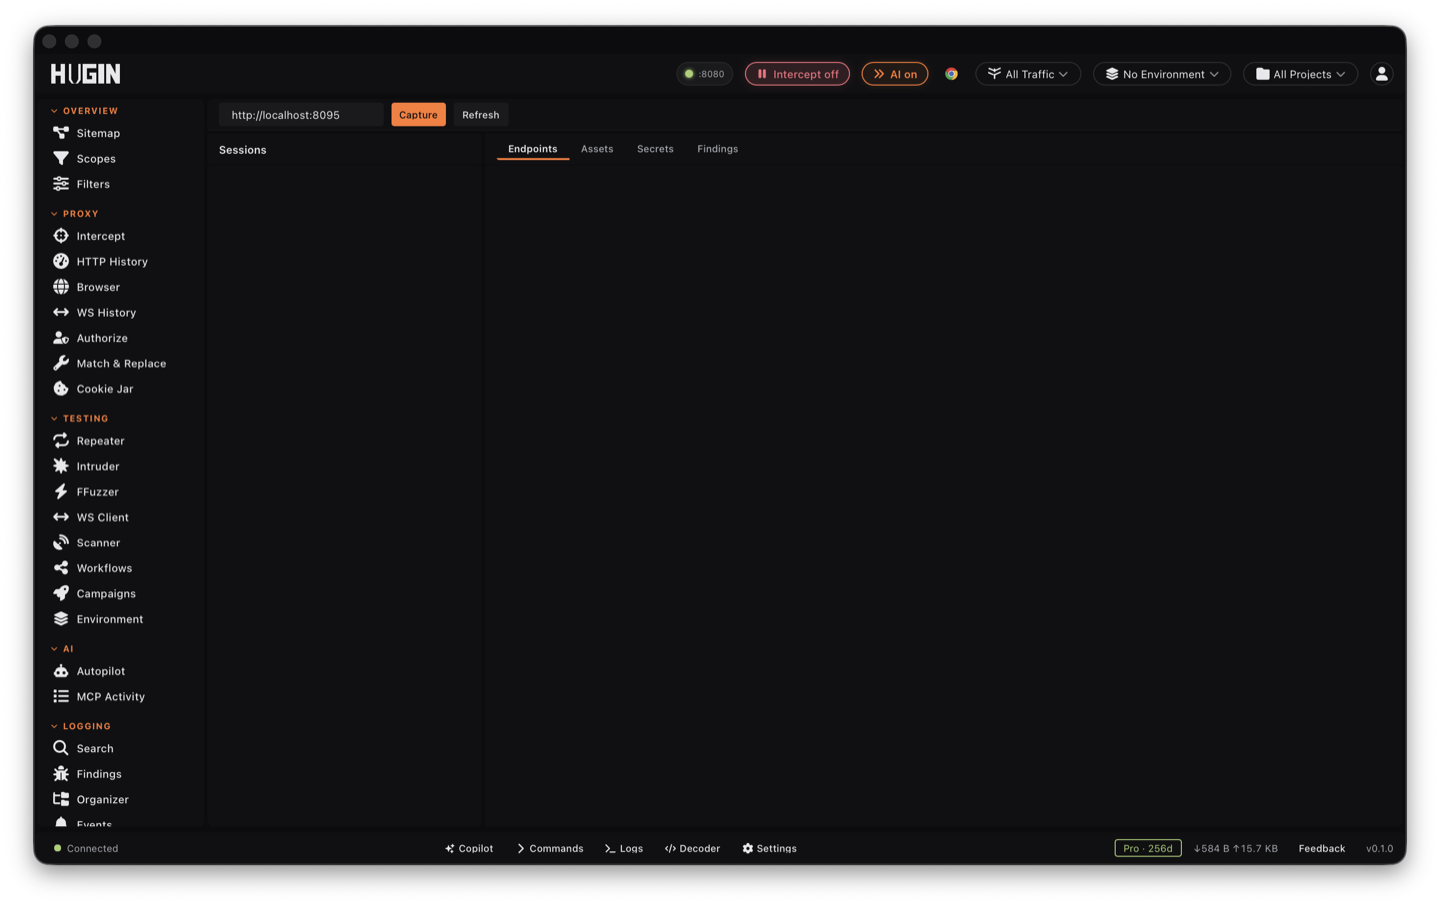
Bundle Engine
Pull apart a target's JavaScript — capture every bundle, reconstruct readable source, and mine the hidden endpoints, secrets, and DOM-XSS the minified code was hiding. (Pro)
Modern apps ship their real attack surface inside minified JavaScript: API routes that never appear in the HTML, parameters the backend quietly accepts, hard-coded keys, and DOM-XSS sinks buried under a webpack build. The Bundle Engine reads that JavaScript for you — it captures every bundle the target loads, reconstructs the original source, and pulls out the endpoints, secrets, and client-side bugs hiding inside. It is a Pro feature.