Mobile app testing
Proxy a mobile app's traffic and drive static + dynamic analysis through the standard mobile toolchain. (Pro)
A mobile app is just another HTTP client, so the same workflow applies: route its traffic through the Proxy and work the flows. Hugin's mobile module is a Pro feature that wraps the standard mobile tools behind one interface — it drives ADB, jadx, apktool, Frida, objection, libimobiledevice, and radare2, so you need those installed.
Get the traffic
Proxy the device
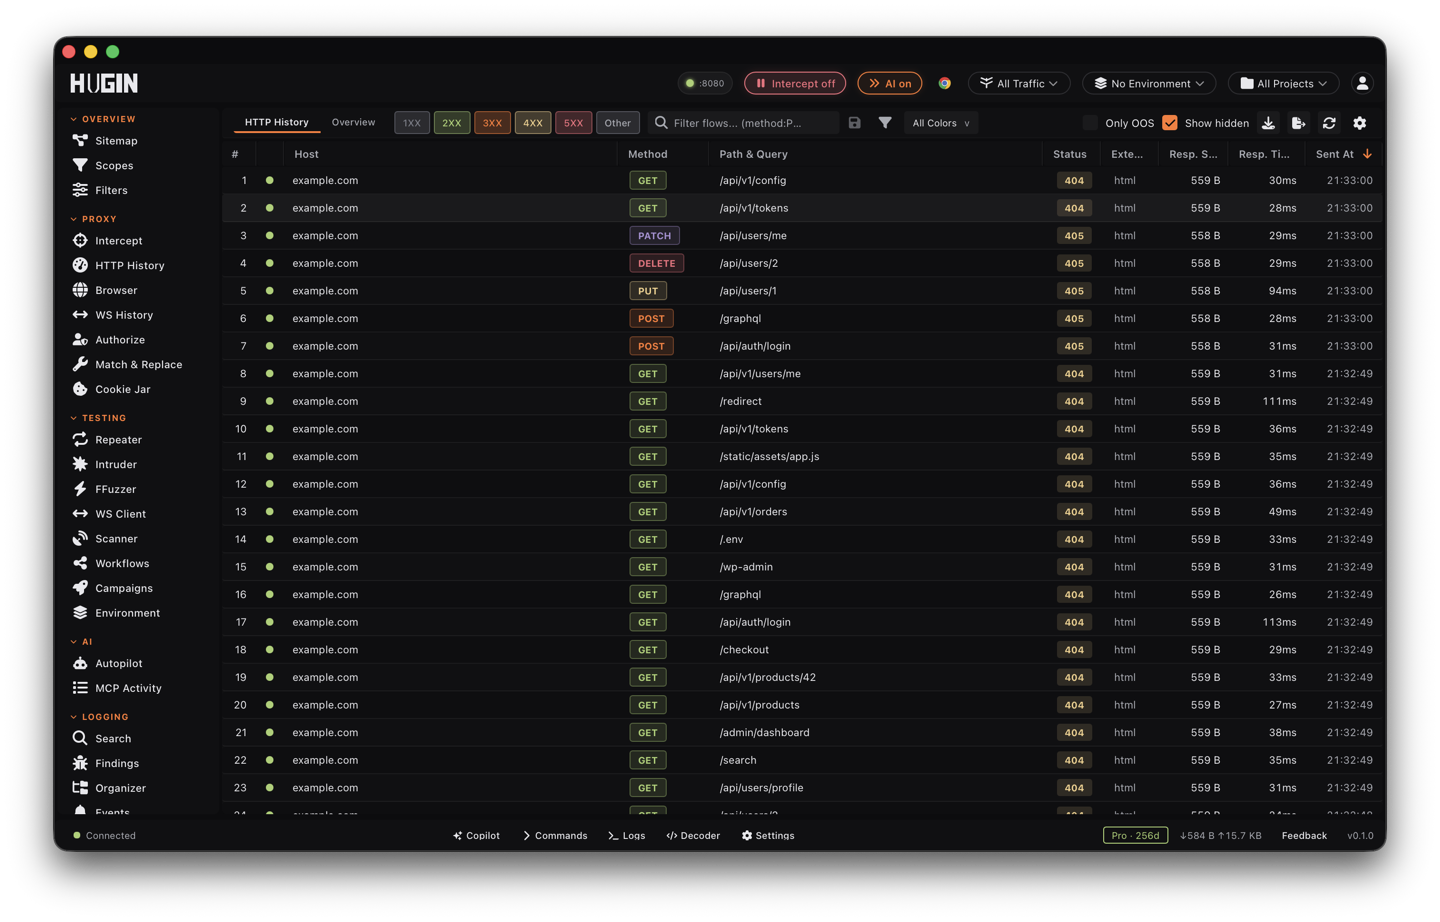
Point the phone's network at Hugin's Proxy and install the CA certificate on the device so HTTPS decrypts.
Beat certificate pinning
Many apps pin their certificate and refuse a proxy. Use the Frida/objection integration to hook the pinning check at runtime so traffic flows into History.
Test the flows
From here it's the usual loop: send mobile API requests to Repeater, fuzz with Intruder, scan the endpoints.
Static and dynamic
The mobile views drive static analysis of the APK or IPA (decompile,
MASVS-style checks, secret scanning) and dynamic analysis on a device or
emulator (Frida, objection). Findings surface in the Mobile views, backed by the
/api/mobile API.
The bug is usually in the API, not the app. Get past pinning, capture the mobile endpoints, and treat them like any other web target.